
Datensicherheit & Datensteuerung
Wie Datenklassifizierung, Zugriff und Kontrollen zu Datensicherheit und Datensteuerung beitragen.
This topic describes development or product direction. It does not confirm availability in your environment.
On this page
The end-to-end data-control model is product direction. Current component security instructions remain available in their product guides.
Navigation und Seitenzusammenfassung sind auf Deutsch. Der technische Inhalt dieser Seite ist vorläufig noch auf Englisch und wird schrittweise übersetzt.
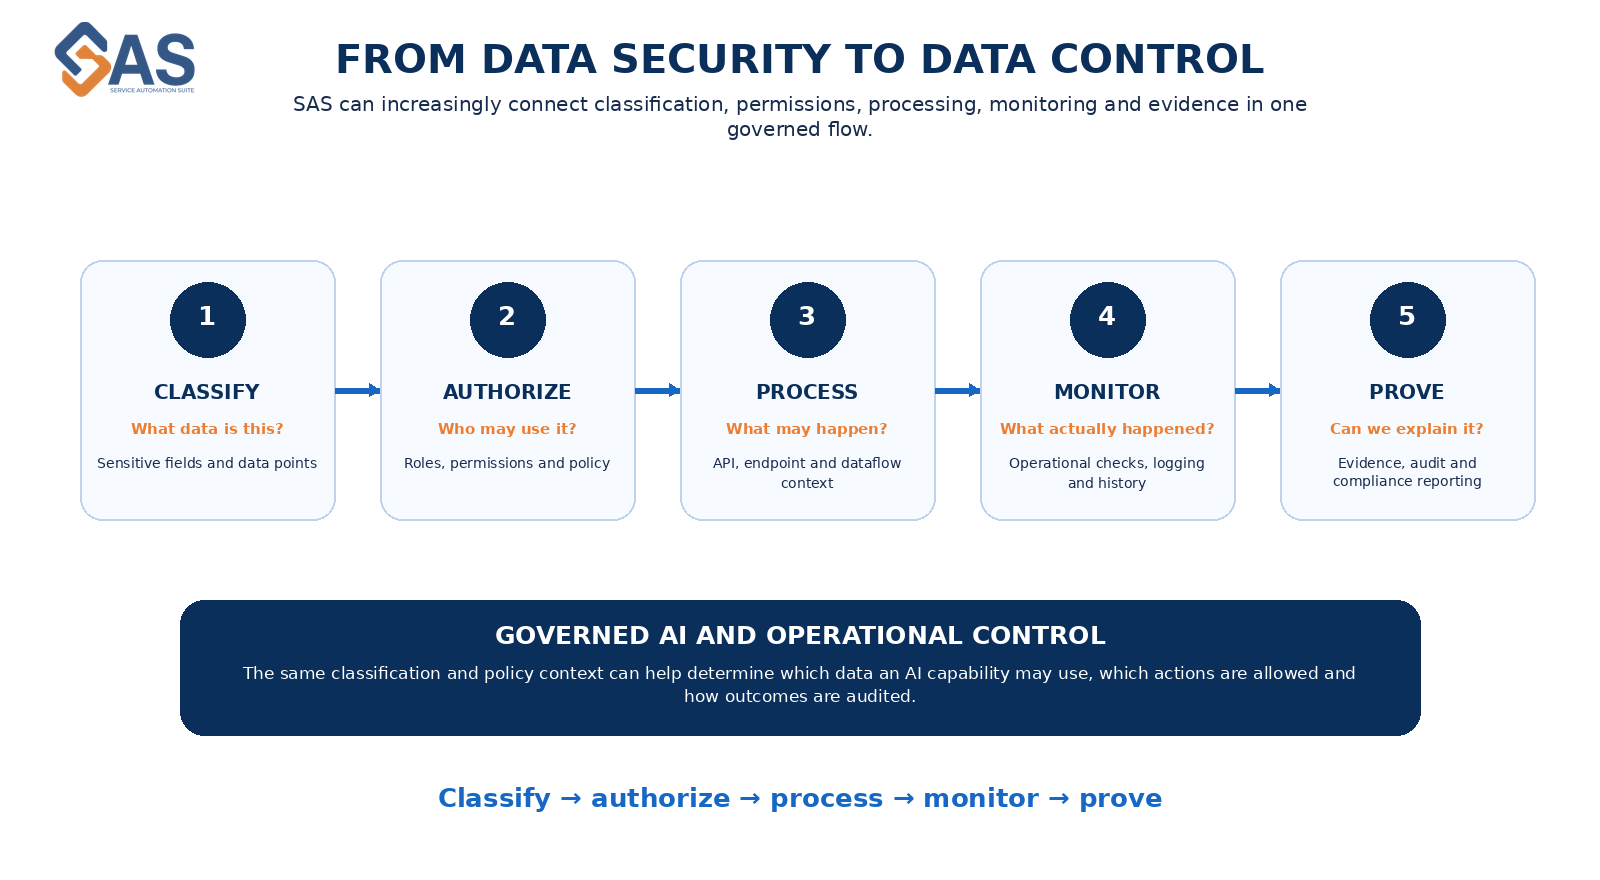
Data security is not limited to controlling who may open a module. A complete control model asks:
- Which data is processed?
- How is it classified?
- Who may use it and for what purpose?
- Where may it be sent or stored?
- What actually happened?
- Can the organization prove that the handling matched policy?
How SAS components contribute
| Capability | Data-control role |
|---|---|
| Data classification | Identifies sensitive fields and required handling |
| API and Endpoint Composer | Makes inbound and outbound data movement explicit |
| Dataflow Composer | Shows how data is selected, joined, transformed, and output |
| Permissions and security profiles | Restrict who may configure or call a capability |
| Policy and controls | Define allowed use and expected outcome |
| Operational Activities | Recheck the actual situation periodically or on an event |
| Logging, history, and evidence | Explain what happened and support audit |
| Governed AI | Restrict which data and actions an AI capability may use |
Platform-wide policy, control, and governed-AI behavior is product direction. Current component-specific security behavior remains the source of truth.
Take the next step
Use the reference material for details or discuss your question with the team.
Ask your question